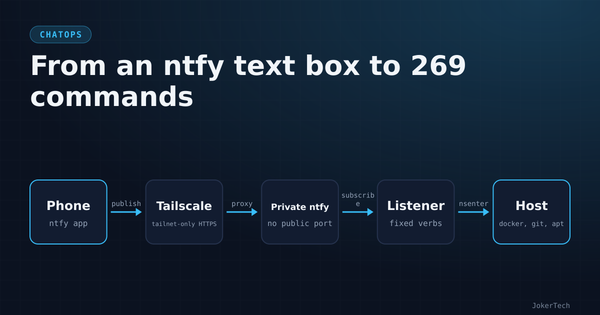
self-hosting Why I run my VPS from a chat topic on my phone instead of SSH How a question about logging expenses from my phone became a ChatOps listener on a private ntfy server: rebuilt four times in a day, then broken in four instructive ways once it met the real server.
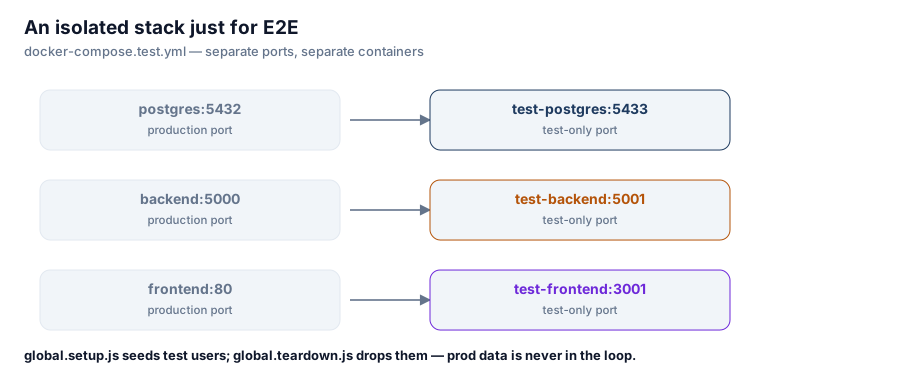
testing An Isolated Docker Test Environment So E2E Tests Don't Touch Prod Data docker-compose.test.yml spins up a second, port-shifted copy of the whole stack just for Playwright, with global.setup.js seeding test users and global.teardown.js cleaning them up.
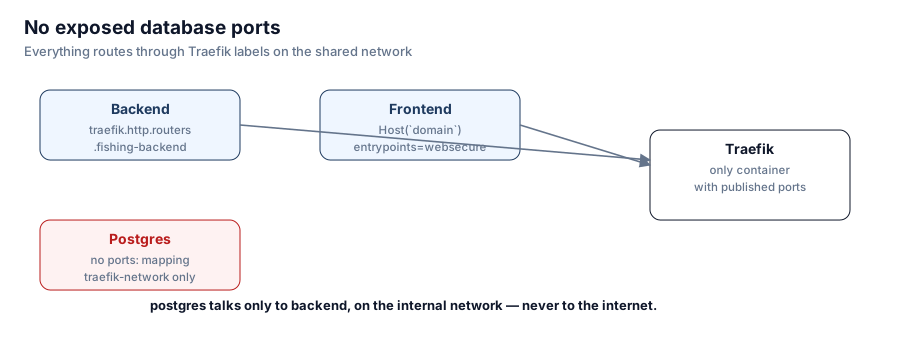
devops No Exposed Database Ports: Routing Everything Through Traefik Labels The production docker-compose for Fishing Tracker Pro publishes zero ports except Traefik's own. Postgres, backend, and frontend are reachable only through label-based routing on a shared Docker network.
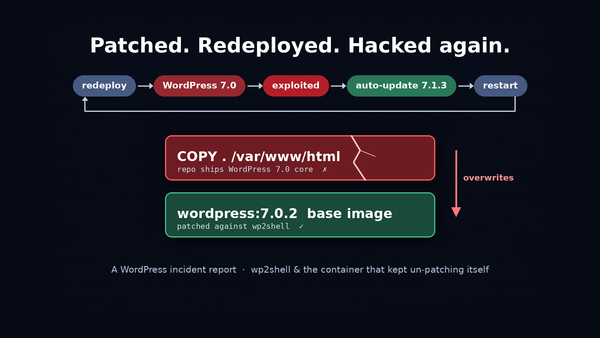
security Patched, Redeployed, Hacked Again: How a Docker Image Kept Un-patching WordPress We cleaned a compromised WordPress site, redeployed, and were breached again two hours later. The cause wasn't a new zero-day. It was our own Dockerfile.
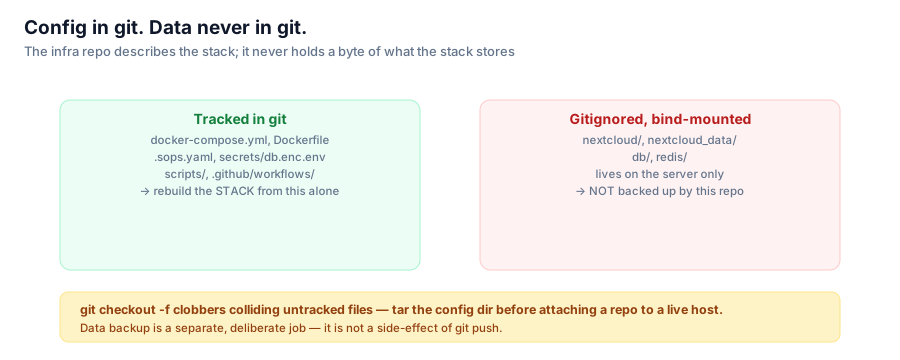
docker Why the Infra Repo Should Never Contain Your Data nextcloud/, nextcloud_data/, db/, and redis/ are bind-mounted directories that live entirely on vmi2633427, are gitignored on purpose, and are explicitly not backed up by the repo that describes the stack running on top of them.
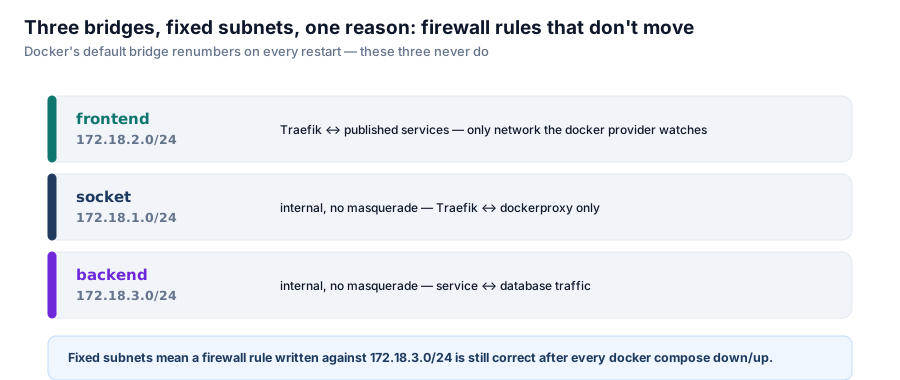
docker Three Docker Networks, Fixed Subnets, One Reason: Firewall Rules That Don't Move frontend, socket, and backend are declared with fixed CIDR blocks on vmi2633427 for a reason that has nothing to do with routing and everything to do with what a firewall rule can trust.
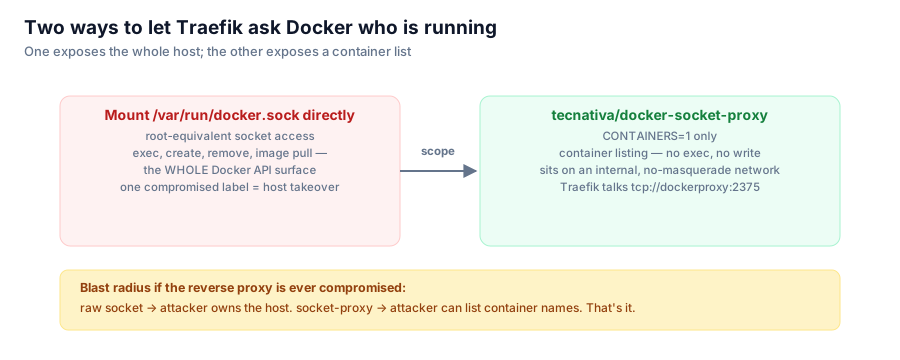
docker Don't Give Your Reverse Proxy Root on the Host Traefik needs to know which containers exist and what labels they carry — it does not need exec, write, or image management. tecnativa/docker-socket-proxy is the difference between those two things.