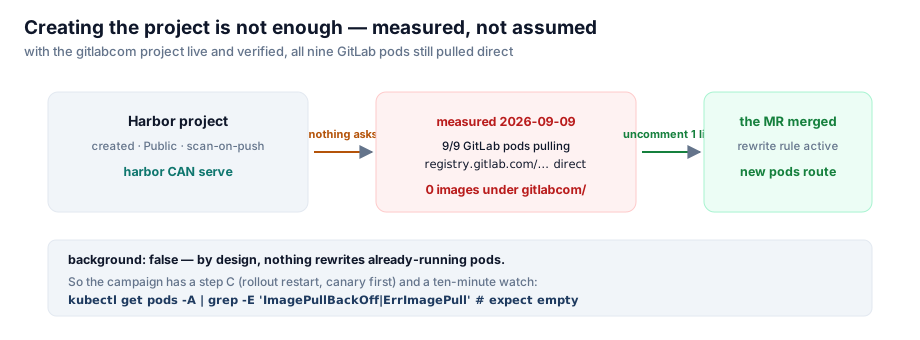
kubernetes Creating the Project Is Not Enough: Measuring the Gap Between Can and Does With the gitlabcom project created, Public and verified, all nine GitLab pods still pulled from registry.gitlab.com directly. Measured on 2026-09-09 — the MR that enables the Kyverno rule is the step that changes anything.
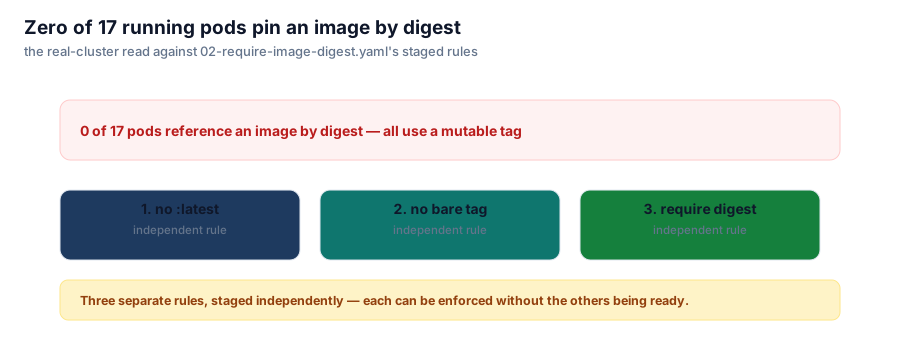
kyverno Zero of 17 Pods Pin a Digest A read-only Kyverno run against the real Pods in a namespace found 17 Pods and zero pinning an image by digest. That number is why the digest policy ships as three separate rules instead of one.
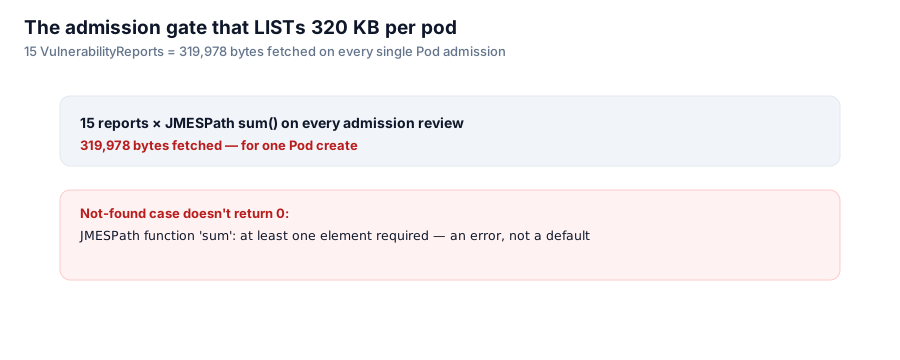
kyverno The Admission Gate That Lists 320 KB Per Pod A Kyverno policy that blocks Pods on CRITICAL CVE counts has to LIST every VulnerabilityReport in the namespace on every admission — 319,978 bytes for 15 reports. And the unscanned case, which should return zero, errors instead.
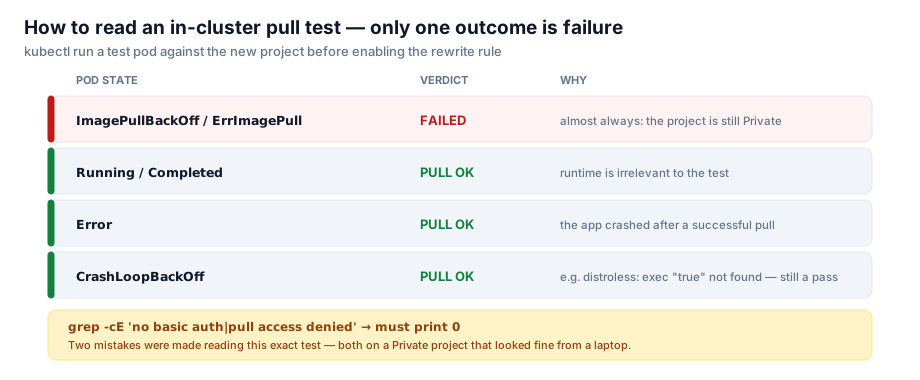
kubernetes The Pull Test: How to Read a Pod Until It Tells You the Truth Only one pod state means the pull test failed. Running, Completed, Error and even CrashLoopBackOff are all passes — and misreading that distinction is how two routing mistakes got through.
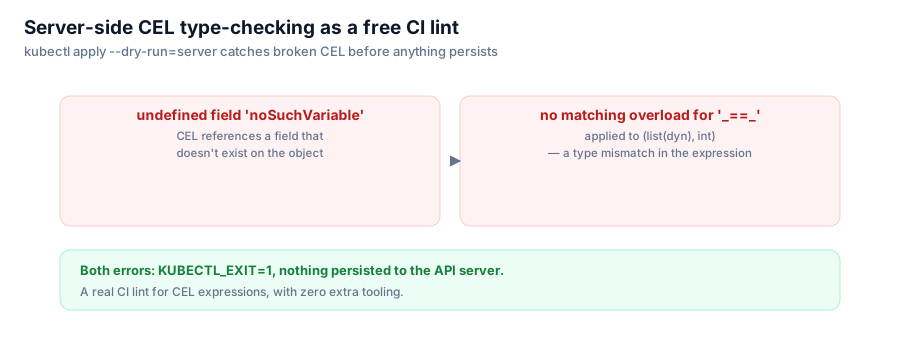
cel Server-Side CEL Type-Checking as a CI Lint kubectl --dry-run=client accepts a ValidatingAdmissionPolicy with a broken CEL expression. --dry-run=server compiles it, names the column of the error, and exits 1 — with nothing persisted. That is a free CI lint.
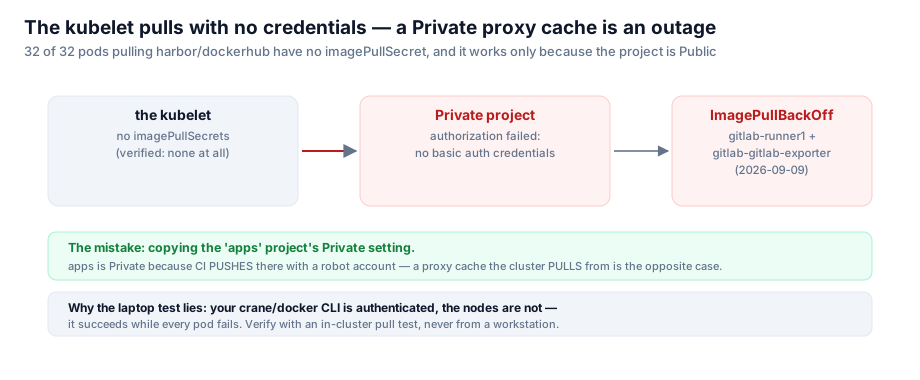
kubernetes Public Project or Nothing: The Proxy-Cache Setting That Is Not a Preference The kubelet pulls with no imagePullSecrets at all — 32 of 32 pods pull from harbor/dockerhub and it works only because the project is Public. Copying the 'apps' project's Private setting took two workloads down.
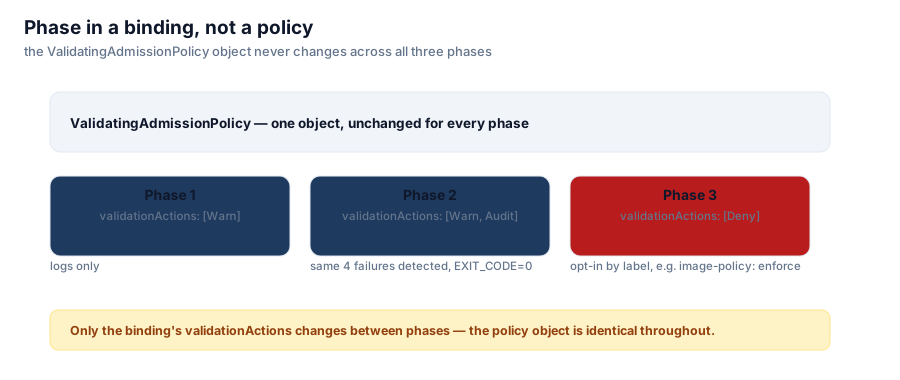
vap Phase In a Binding, Not a Policy With native VAP, the grace period lives in the binding's validationActions, never in the policy object. The same four violating Pods still report as failures under [Warn, Audit] — but the run exits 0, and phase 3 is opt-in by namespace label.
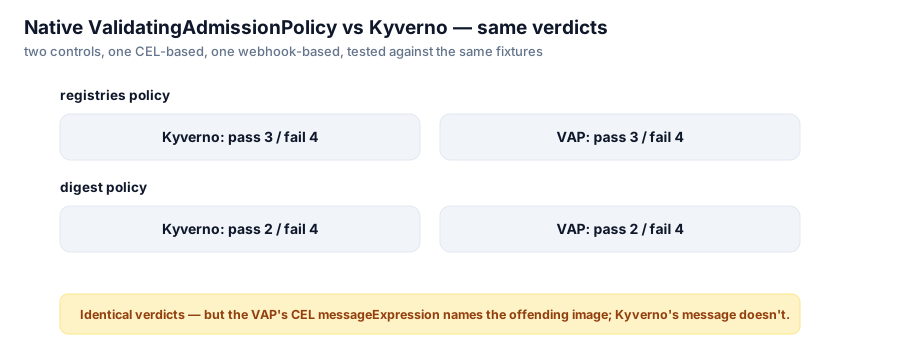
vap Native ValidatingAdmissionPolicy vs Kyverno, Same Two Controls The registry allow-list and the digest-pinning control were reimplemented as native CEL ValidatingAdmissionPolicies and run against the identical fixtures. Same verdict on every Pod — and CEL's messageExpression names the offending image.
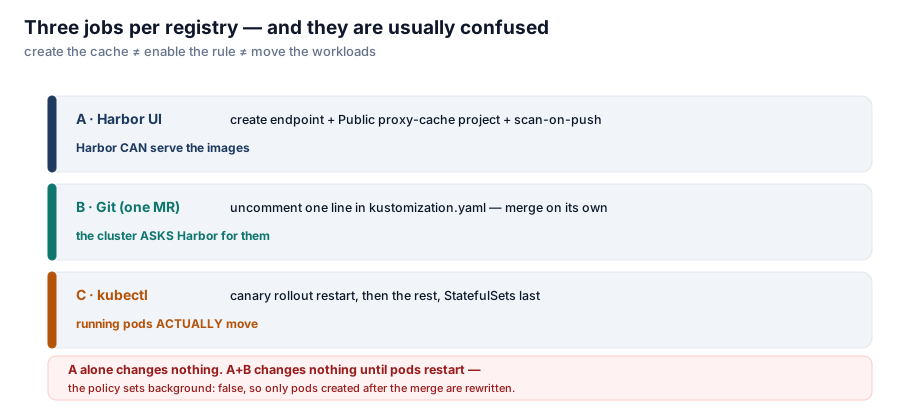
platform-engineering The Registry Routing Campaign: Two of Nine, and Why It Goes One at a Time Routing upstream registries through Harbor is three separate jobs per registry — create the cache, enable the rule, move the workloads — and the campaign only works done one registry at a time, safest first.
GCP Implement DevOps Workflows in Google Cloud: Challenge Lab This is from the Arcade October 2024 Series and also Implement DevOps Workflows in Google Cloud course. This tutorial covers the Lab "Implement DevOps Workflows in Google Cloud: Challenge Lab", code: GSP330. Overview In a challenge lab, you’re presented with a scenario and a series of tasks.
GCP Continuous Delivery with Jenkins in Kubernetes Engine This is from the Arcade October 2024 Series. This tutorial covers the Lab "Continuous Delivery with Jenkins in Kubernetes Engine", code: GSP051. We will learn how to use Jenkins to set up a continuous delivery pipeline on the Kubernetes engine. Developers who often integrate their code in a