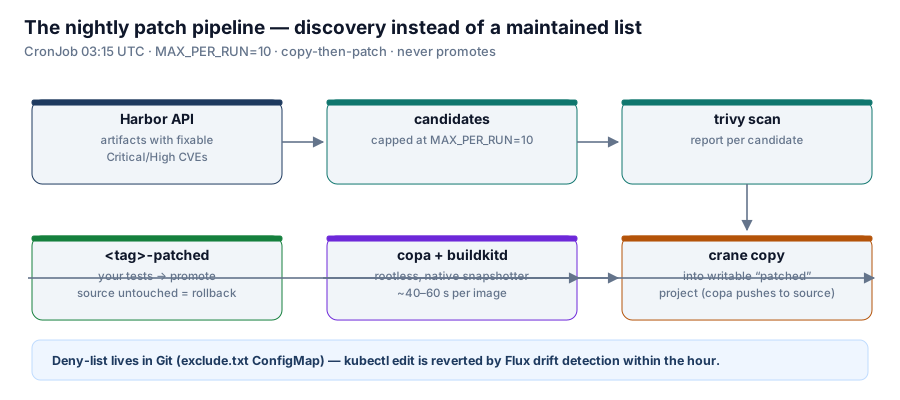
containers Patching Without a List: A Nightly Pipeline That Finds Its Own Targets Every image list you maintain by hand is stale the day after you write it. Our Copacetic pipeline discovers candidates from Harbor's own scan results instead.
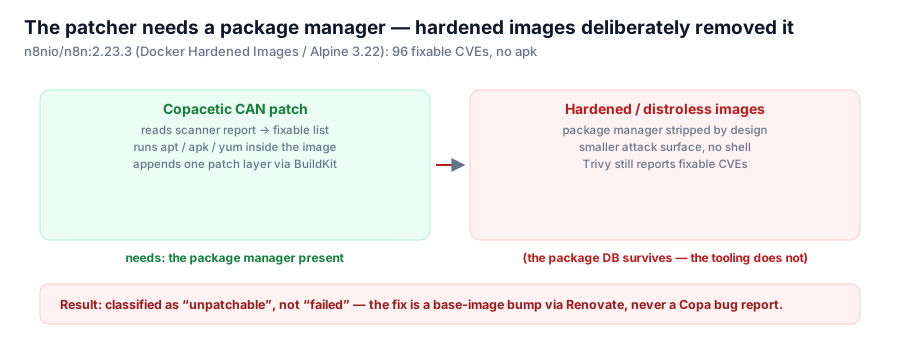
containers Your Most Secure Images Are the Ones Copacetic Can Never Patch Hardened and distroless bases strip the package manager, which means Copacetic has nothing to run. 96 fixable CVEs, no apk, and the right response is a base bump, not a Copacetic bug report.
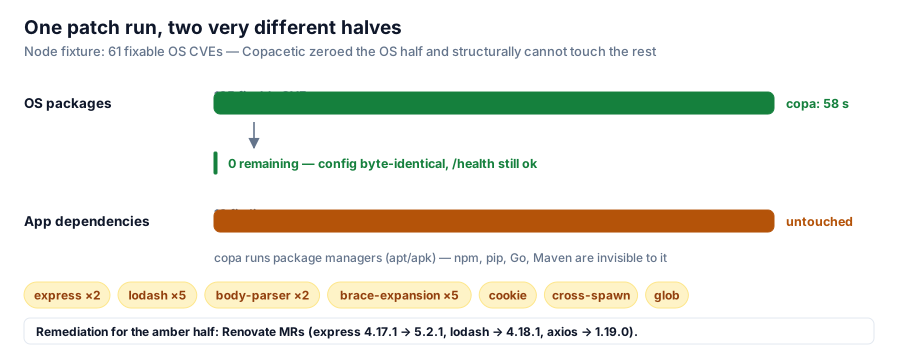
containers 105 CVEs to Zero in 40 Seconds: What Copacetic Actually Does to an Image Copacetic patched every fixable OS CVE on our fixtures without a rebuild — and left every application dependency untouched. Both halves of that sentence matter.
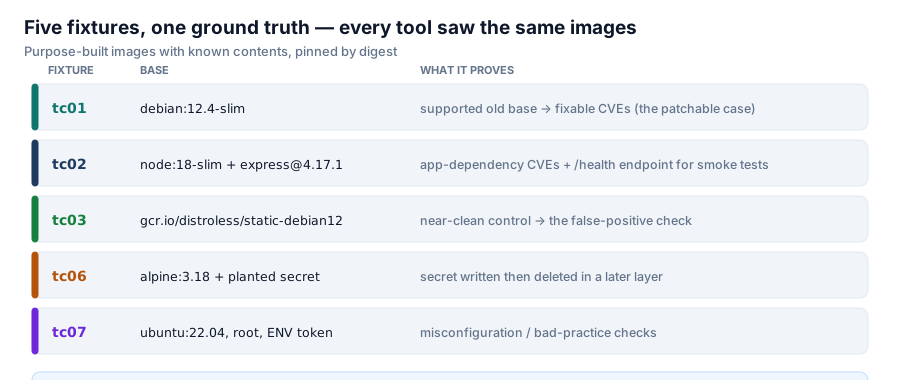
containers Build the Fixtures Before the Tools: A Testing Methodology for Container Scanners A scanner comparison against whatever happens to be running is a number, not a comparison. Here is the fixture set — known-bad images pinned by digest — that makes tool claims testable.