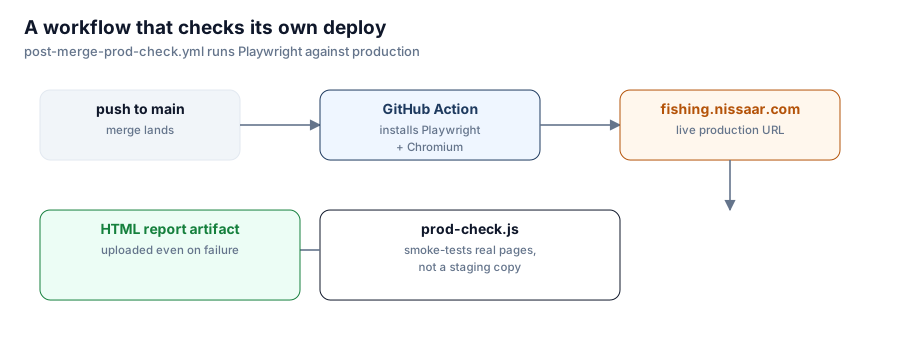
ci-cd A GitHub Action That Checks Your Own Deploy After It Ships post-merge-prod-check.yml runs a small Playwright script against the real fishing.nissaar.com URL after every push to main — because a green CI build says nothing about whether the deploy actually worked.
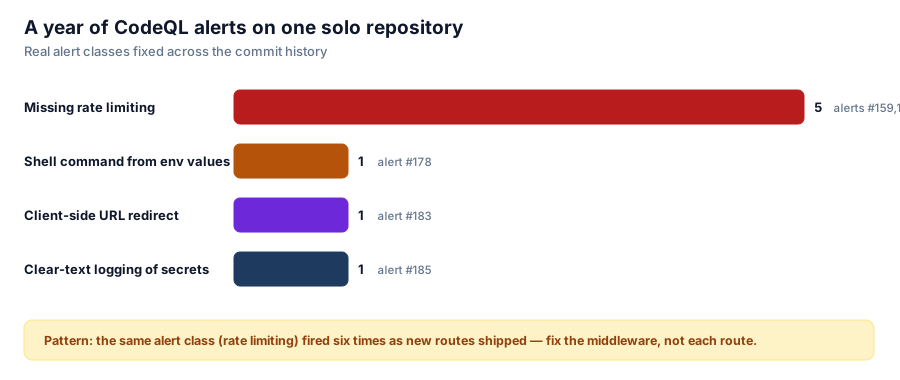
security What a Year of CodeQL Alerts Looks Like on a Solo Project Eight code-scanning alerts, four distinct classes, fixed one at a time across a year of commits — the real pattern is that rate limiting had to be fixed six separate times before it stuck.